


Every day, enterprise security teams wake up to a familiar scene: a flood of vulnerability findings from scanners and asset inventories, a backlog that grows faster than teams can respond to, and a mounting question: what actually gets fixed — and how fast at scale?
In a world of multi-cloud architectures, container fleets, thousands of microservices, and continuous deployment, the old model of “scan → triage → ticket to IT or dev” is collapsing under its own weight.
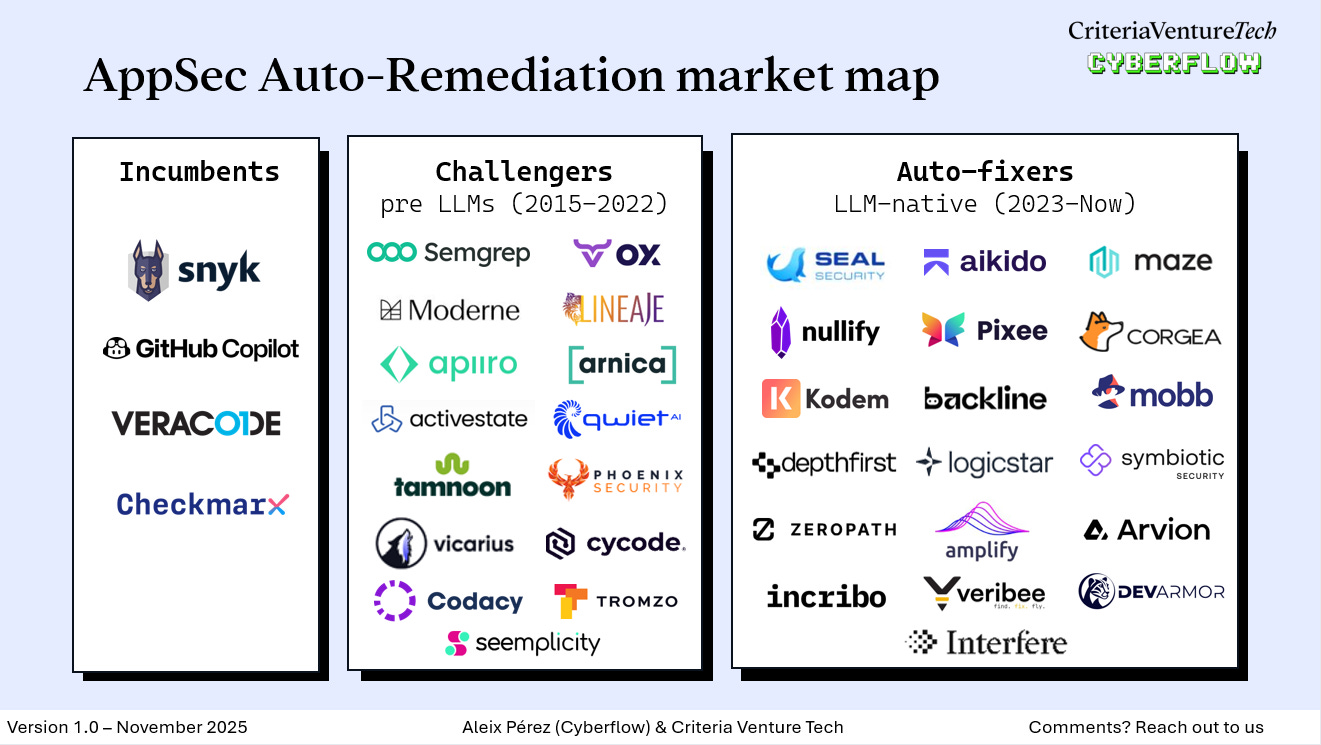
This is the environment fueling a wave of innovation in auto-remediation — tools that don’t just detect vulnerabilities, but automatically or semi-automatically fix/remediate them. To make sense of the expanding vendor ecosystem, we’ve created an AppSec Auto-Remediation Market Map, categorizing companies into Incumbents, Challengers, and the new generation of LLM-native Auto-Fixers.
📩 Building in the space? We’d love to hear from you! Reach out Aleix Perez (aperez@caixacapitalrisc.es)
1. Why Now? The Remediation Bottleneck
Five forces are converging to make remediation automation not just attractive — but necessary:
Backlog Explosion
Vulnerability volumes keep rising as cloud, container, serverless, and IoT adoption expands the attack surface. Traditional scanning and ticketing can’t keep pace.
Speed of Exploitation
Many vulnerabilities are exploited within days or even hours of public disclosure. Remediation velocity — not just detection velocity — now determines breach risk.
Human-Capacity Constraints
Security, operations, and development teams are already overstretched. Manual patching and ticket routing consume scarce talent that organizations can’t scale linearly.
Technological Enablers
APIs, workflow engines, patch-automation tools, and now generative AI make automated analysis and code-level remediation increasingly feasible. Continuous deployment pipelines also create natural insertion points for automated fixes.
Governance & Risk Pressure
Boards, CISOs, insurers, and regulators are asking harder questions: Which vulnerabilities were fixed? How long did it take? Which were auto-remediated?
Visibility and auditability have become mandatory.
The result: remediation is transitioning from “nice to have” to “must-have.” And vendors are racing to define the next generation of AppSec.
2. Mapping the Auto-Remediation Landscape
The market has evolved in clear waves, each marking a leap in automation and intelligence. Our map organizes vendors into three eras:
Wave 1 — The Incumbents (Pre-LLM AppSec Foundations)
Companies: Snyk, GitHub (Advanced Security), Veracode, Checkmarx
These companies built the foundation of modern AppSec: scanners, dependency analysis, and developer-friendly workflows. Their strength lies in detection, prioritization, and code insights — but fixes typically still require human involvement.
They are the classic “remediation helpers”: excellent visibility, strong platform adoption, but not yet fully autonomous remediation.
Wave 2 — The AppSec Challengers (Pre-LLMs, 2015-2022)
Companies: Semgrep, OX Security, Moderne, Lineaje, Apiiro, Arnica Security, Tromzo, ActiveState, Qwiet AI, Phoenix Security, Tamnoon, Cycode, Vicarius, Codacy, Seemplicity
This wave consists of the pre-LLM innovators that pushed AppSec beyond basic scanning and into the era of context, prioritization, and workflow automation.
These companies were built before generative AI became mainstream, relying instead on static analysis, heuristics, ML classifiers, graph analysis, and rule-based engines. They are not LLM-native, but many are now layering AI on top of their original platforms or fully pivoting their products to become LLM-native.
They bridge the gap between detection and automation by focusing on:
1. Risk Prioritization & Correlation
They analyze vulnerabilities across multiple scanners (SAST, SCA, IaC, cloud, container, supply chain) and prioritize them using business context, exploitability, reachability, asset value, and code ownership.
2. Workflow Orchestration & Consolidation
They integrate findings across tools, reduce noise, group duplicates, map issues to teams, and push fixes into developer backlogs.
3. Early Automation & Assisted Remediation
Some vendors began offering code suggestions, dependency updates, secure build pipelines, or workflow-driven remediation steps — but not yet full autonomous code fixing.
Automated dependency patching: ActiveState
Script-based remediation & patch automation: Vicarius
Targeted code-level fixes: Semgrep, Arnica, Apiiro
Large-scale refactoring & modernization: Moderne
4. Developer-Centric Security
Many platforms in this group were built to integrate directly with Git, CI/CD, or developer workflows — reducing friction compared to traditional AppSec.
Wave 3 — The Auto-Fixers / AI AppSec Engineer (LLM-Native, 2023–Now)
Companies: Seal Security, Aikido Security, Maze AI, Nullify, Pixee, Corgea, Kodem, Backline, Mobb, Depthfirst, Logicstar, Symbiotic Security, Zeropath, Amplify Security, Arvion, Incribo, Veribee, DevArmor, Interfere
Wave 3 represents the first true generation of LLM-native security platforms — vendors founded or reshaped after 2023, built from the ground up around generative AI, automated code remediation, and autonomous fix workflows.
Where Wave 2 optimized “what to fix,” Wave 3 focuses on fixing it, automatically, safely, and at scale.
These companies, also named AI AppSec Engineers, move vulnerability management from assisted to autonomous by focusing on:
1. AI-Generated Fixes & Patch Creation
These tools generate code or configuration fixes directly from scanner findings — including SAST, SCA, IaC, container scans, and cloud misconfigurations. Fixes are delivered as ready-to-merge PRs, automated patches, or directly applied changes.
2. Autonomous Remediation Pipelines
Beyond generating fixes, many Auto-Fixers automatically apply, test, and validate patches across repositories, services, and environments. They often integrate rollback mechanisms and guardrails to ensure safe application.
3. Cross-Domain Coverage
Auto-Fixers often support multiple scanners via a unified Fix API, handling vulnerabilities across first-party code, dependencies, containers, IaC, cloud misconfigurations, and OS packages.
4. Developer-Minimal or Developer-Optional Workflows
Fixes appear directly in GitHub/GitLab pull requests, CI/CD pipelines, and SCM workflows — requiring minimal human approval. Many tools support 1-click fixes, bulk remediation, and hands-free workflows for high-confidence patterns.
5. Early-Stage Innovation & Rapid Expansion
The Auto-Fixer category is young, fast-moving, and attracting strong venture interest. Most companies in this wave were founded post-2023 or pivoted to LLM-native remediation after the generative AI inflection point.
They represent the emerging “99% Auto-Fix” vision for remediation.
Vendor Differentiators to Watch
Scanner & Language Coverage (SAST, SCA, IaC, cloud-native; Java, Python, JS, Go, etc.)
Depth of Fix Automation (Fix suggestions → ready-to-merge PRs → autonomous patching & validation)
Technical Approach (Rule-based, LLM-based, or hybrid deterministic pipelines)
Safety and Guardrails (Rollback mechanisms, approval workflows, audit logs)
Business-Risk Alignment (Fixing what actually reduces organizational risk)
DevOps Integration Depth (Git, CI/CD, ServiceNow, Jira — enabling true shift-left remediation)
What Ultimately Matters: Auto-Fix Accuracy, Autonomy, Speed & % Fully Auto-Fixed
At the end of the day, this is the metric that separates real Auto-Fixers from noise:
How accurately, safely, quickly, and autonomously the platform can fix vulnerabilities — and what percentage of your findings it can remediate end-to-end without human intervention.
High accuracy + autonomy + speed + coverage = the foundation of the next generation of AppSec platforms.
Conclusion
The market’s evolution is now clear:
Incumbents built the detection and AppSec ecosystem.
Challengers introduced workflow and early automation.
Auto-Fixers — LLM-native Code-Fixers — are redefining the category by closing vulnerabilities autonomously.
The shift from “scan → ticket → fix” to “scan → prioritise → auto-remediate (with guardrails)” is already underway. Our vendor map captures this moment, but the real story is the acceleration toward higher automation, developer integration, and business-risk-aware remediation.
Enterprises that embrace auto-remediation early will dramatically increase remediation velocity, reduce backlogs, and free developers from the endless tax of manual security fixes.
As vulnerability volume accelerates, one thing is now clear:
it’s no longer enough to detect and report — you must fix, and you must fix fast.
The era of automated remediation has arrived, and the companies on this map are building its foundation.
📩 Building in the space? We’d love to hear from you! Reach out Aleix Perez (aperez@caixacapitalrisc.es)

It’s nice if you got tools auto fixing findings, but I think it becomes problematic if they don’t include a feedback loop for developers to actually learn and don’t produce the same finding again. I think it will make many developers just dependent on those tools, no longer thinking for themselves and burning tokens instead of actually learning to write secure code.
Great work! Keep it up pls