


Every CISO knows the ritual. Once a year, sometimes twice if the budget allows, a team of penetration testers shows up, spends two to four weeks poking at a subset of the infrastructure, delivers a PDF, and disappears. Six months later, the environment has changed so much that half the findings are stale and half the new attack surface was never tested.
That model is now breaking. When AI-powered attacks move from compromise to exfiltration in under 30 minutes, and when Anthropic’s Mythos can autonomously chain four vulnerabilities into a browser sandbox escape overnight, annual pentesting is no longer a security strategy. It’s a compliance ritual.
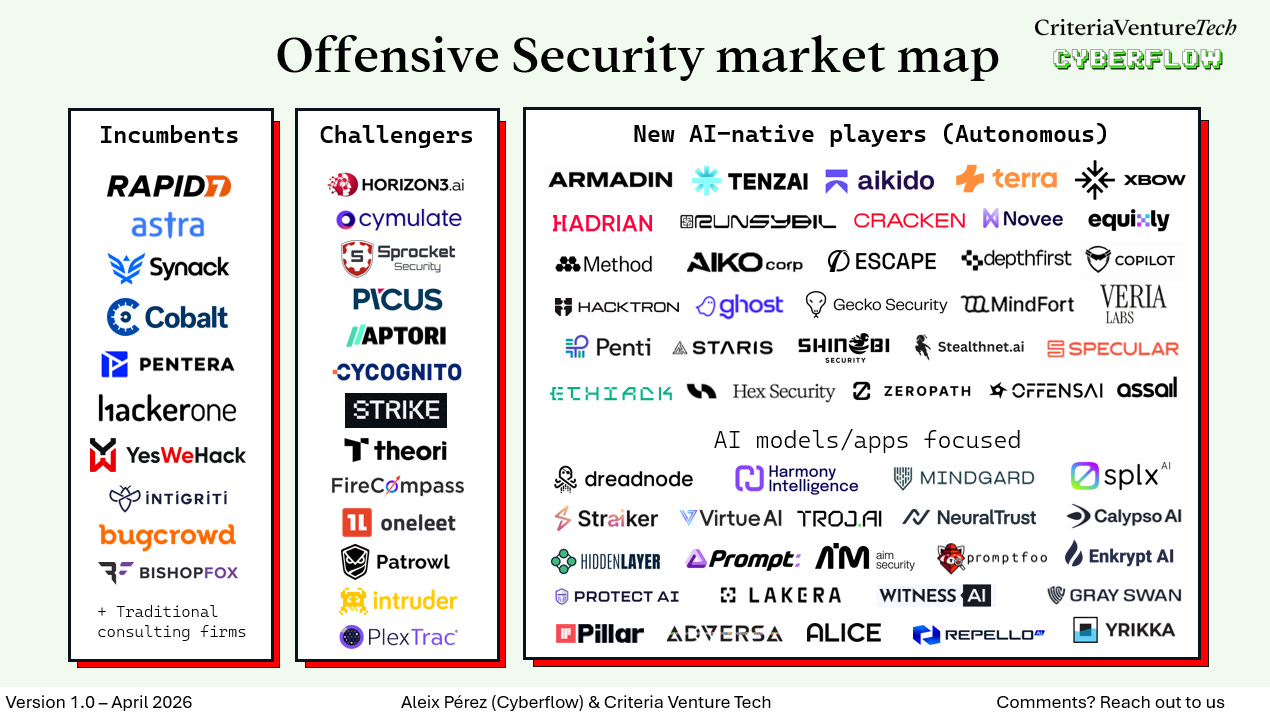
A new category is emerging — Autonomous Offensive Security — and it’s attracting some of the largest early-stage rounds in cybersecurity history. To make sense of the rapidly expanding vendor ecosystem, we’ve created an Offensive Security Market Map, categorizing companies across three waves: Incumbents, Challengers, and the new generation of AI-native autonomous players.
📩 Building in the space? Reach out — Aleix Perez (aperez@caixacapitalrisc.es
)
1. Why now? The offensive security inflection point ❓
Five forces are converging to make autonomous offensive security not just attractive, but necessary:
The speed gap is now untenable. Attackers powered by AI move at machine speed. CrowdStrike’s 2026 Global Threat Report documented an 89% increase in AI-enabled attacks, with average breakout times dropping to 29 minutes. Annual pentests that take weeks to schedule and execute can’t defend against adversaries that operate 24/7 at the speed of API calls.
Code volume is exploding. With more than 30% of new code now generated by AI, and enterprises deploying updates multiple times per day, the gap between what gets built and what gets tested is widening by the hour. Vibe coding has made software creation accessible to people who were never trained to think about security. The attack surface grows faster than any human team can audit.
The talent shortage is structural. The penetration testing market is estimated at $2.4–2.7 billion in 2025, growing at 12–15% CAGR. But most of this market still depends on a small pool of elite human testers. With 4.8 million unfilled cybersecurity positions globally, and offensive security expertise being the scarcest skillset of all, scaling through hiring is impossible.
Frontier models changed the game. Anthropic’s Mythos Preview found thousands of critical zero-days across every major operating system and browser — capabilities that emerged from general reasoning improvements, not specialized offensive training. If a general-purpose model can do this, purpose-built offensive AI agents will go further, faster.
The asymmetry structurally favors offense. Research from Anthropic and Google DeepMind shows that offensive operations produce immediate, verifiable feedback (breached or not), making them ideal for reinforcement learning. Defense has no equivalent signal. AI-generated phishing went from underperforming human red teams by 18% to outperforming them by 24% in just two years. The feedback loop is accelerating.
Regulation demands continuous validation. PCI DSS 4.0, NIS2, DORA, and HIPAA now require structured, auditable security testing. Compliance-driven demand is pushing organizations from ad-hoc annual tests to continuous offensive security programs.
The result: pentesting is transitioning from an episodic consulting engagement to an always-on, AI-powered security function. The companies in this map are building that future.
2. The Three Waves 🌊
Wave 1 — Incumbents (Pre-2015)
Rapid7, Astra, Synack, Cobalt, Pentera, HackerOne, YesWeHack, Intigriti, Bugcrowd, BishopFox
The foundation of modern offensive security: managed pentesting platforms, bug bounty marketplaces, and BAS tools. Strong brand, deep distribution, large researcher networks, but fundamentally human-dependent. Bug bounty platforms rely on crowdsourced researchers. Managed pentest firms sell consultant hours. Even BAS players like Pentera run predefined scenarios rather than reasoning through novel attack paths.
Several are evolving, Pentera has acquired AI capabilities, Cobalt moved toward PTaaS, HackerOne is integrating AI triage, but the underlying architecture was not built for autonomous, continuous operation.
Wave 2 — Challengers (2015–2023)
Horizon3.ai, Cymulate, Sprocket Security, Picus, Aptori, CyCognito, Strike, Theori, FireCompass, Oneleet, Patrowl, Intruder, PlexTrac
Pre-LLM innovators that pushed beyond manual pentesting into automation, continuous testing, and attack surface management. Horizon3.ai and Cymulate pioneered continuous validation. CyCognito and FireCompass built external attack surface discovery. Picus and Cymulate created BAS platforms mapped to MITRE ATT&CK. PlexTrac streamlined reporting and remediation workflows.
Many are now layering AI on top of existing platforms, but their core architectures were not designed for the agentic, reasoning-based approach that defines the next generation.
Wave 3 — Autonomous Offensive Security (2024–Now)
Armadin, Tenzai, Aikido, Terra Security, XBOW, Hadrian, Runsybil, Cracken, Novee, Equixly, Method, Aiko Corp, Escape, Depthfirst, Copilot, Hacktron, Ghost, Gecko Security, MindFort, Veria Labs, Penti, Staris, Shinobi Security, Stealthnet.ai, Specular, Ethiack, Hex Security, Zeropath, OffensAI, Assail
Plus an AI security sub-segment: Dreadnode, Harmony Intelligence, Mindgard, SPLX AI, Straiker, Virtue AI, Troj.AI, Calypso AI, HiddenLayer, Prompt Security, AIM Security, Enkrypt AI, Protect AI, Repello AI, Yrikka, NeuralTrust, Pillar, Adversa, Alice, Witness AI
The first true generation of AI-native offensive security platforms. Where Wave 2 automated known playbooks, Wave 3 reasons, adapts, and chains attacks like a skilled red teamer, at machine speed, continuously, across the entire attack surface.
What defines them:
Agentic attack swarms. Armadin, led by Mandiant founder Kevin Mandia, backed by $189.9M in the largest seed+Series A in cyber history, deploys specialized AI agents that continuously identify real kill chains. As Mandia put it: “You cannot have a human in the loop for every defense decision and expect to win.”
Validated exploitation, not scanning. XBOW outperformed thousands of human researchers on the HackerOne leaderboard. Their $120M Series C at $1B+ valuation validates the thesis.
Always-on operation. Tenzai, founded by the Guardicore team (acquired by Akamai for $600M), backed by a record $75M seed — builds an autonomous AI hacker that operates continuously. As CEO Pavel Gurvich noted: “Providing real security assurance is only possible with autonomous AI.”
Business context. Terra Security ingests documentation, API schemas, and cloud architecture to differentiate between a critical vulnerability on a sandbox and a medium one on a payment gateway. The “so what?” layer that makes findings actionable.
AI model security. A distinct sub-segment, Mindgard, HiddenLayer, Protect AI, Prompt Security and others, focuses on securing AI models themselves against prompt injection, model theft, and adversarial attacks. This is rapidly growing as enterprises deploy AI agents at scale.
3. The Market Opportunity 📈
The pentesting market is valued at $2.4–2.7 billion in 2025, projected to reach $5.5–7.4 billion by 2031–2034. But the real opportunity is much larger:
Pentesting is just the entry point. Autonomous platforms expand into vulnerability management, red teaming, attack surface management, and security validation — collectively a $15–20 billion opportunity.
Services are the real TAM. As Tenzai’s Gurvich noted: “For every dollar an organization spends on security products, it spends about five on services.” The addressable market is the security services market, not just pentesting software.
The coverage gap is the unlock. Enterprises currently test only 20–25% of applications due to cost constraints. AI platforms enabling 100% coverage unlock 4–5x the current market in latent demand.
The capital flowing in reflects these expectations. Armadin’s $189.9M is the largest early-stage raise in cybersecurity history. The investor thesis is clear: autonomous offensive security is a category-defining opportunity.
4. The hidden battleground: Training data 🛢
Where does the training data come from, and who owns it? This may be the single most important competitive dynamic in the category. The best offensive security data, real exploitation chains, attack decision logic, red team methodologies, sits behind NDAs and in the heads of a few thousand elite practitioners. Unlike NLP or computer vision, there’s no ImageNet for hacking.
Four strategies are emerging:
The open foundation. CVE databases, disclosed exploits, security research papers. Everyone has these — table stakes, zero differentiation.
The expert factory. Hiring elite pentesters to generate labeled training data. Armadin’s approach: “reinforcing decades of human-led red teaming expertise into AI models.” Exceptional quality, but six-figure salaries don’t scale linearly.
The synthetic lab. Multi-agent architectures where AI sub-agents attack and defend against each other via reinforcement learning. Scales beautifully — the question is whether synthetic environments produce patterns that transfer to real-world exploitation.
The crowd. Turning bug bounty communities into data generation engines. Strong network effects, but data is only as valuable as its relevance to your target attack surface.
Our view: narrow data advantages (public CVEs) get compressed as foundation models improve. Proprietary attack methodology captured at scale becomes the defining competitive moat.
5. What happens to pentest services firms? 🧑💻
Manual testing still accounts for ~75% of the market. Most pentesting revenue flows to consulting firms, boutique shops, and Big 4 practices through human labor — thousands of firms billing $150–300/hour for work that is skilled but inherently unscalable.
The disruption math is straightforward. XBOW delivers expert-grade reports starting at $4,000 for assessments that cost $10,000–35,000 from a human team. When output quality converges, and HackerOne leaderboard results suggest it already is, pricing pressure will be severe.
But the story bifurcates, much like the MSSP market under AI pressure:
The firms that adopt get dramatically more efficient. A boutique with 15 pentesters that integrates autonomous platforms could cover 5–10x more clients — using AI for breadth and continuous coverage, deploying humans for the creative work AI can’t replicate: adversarial red teaming, social engineering, physical security, novel attack research. Their value proposition shifts from “we send you people” to “we deliver continuous offensive assurance.”
The firms that don’t adopt get commoditized. Two-week manual engagements and PDF reports compete on price against platforms delivering better coverage, faster, for less. The “annual pentest as compliance checkbox” becomes a race to the bottom.
The winning pentest firms of 2030 will operate as AI-augmented offensive security practices, autonomous platforms as the base layer, human expertise for complex engagements, selling outcomes instead of hours.
6. What comes next 🔮
Within three to five years:
Manual pentesting becomes boutique — reserved for nation-state-grade red teaming, custom hardware, and classified environments. Everything else goes autonomous.
Continuous offensive security becomes standard — integrated into CI/CD, triggered at every deployment, running 24/7. The “annual pentest” becomes as antiquated as annual antivirus scans.
Offensive and defensive merge — the next great security company will combine vulnerability management, threat hunting, pentesting, and offensive security into a continuous loop.
Incumbents acquire or get displaced. Wave 1 players with distribution but legacy architectures will either buy Wave 3 technology or lose relevance.
The era of the AI red team has arrived. The companies on this map are building its foundation.
📩 Building in the space or want to discuss the market? Reach out — Aleix Perez (aperez@caixacapitalrisc.es)
